Lab: inside, outside, and a DMZ
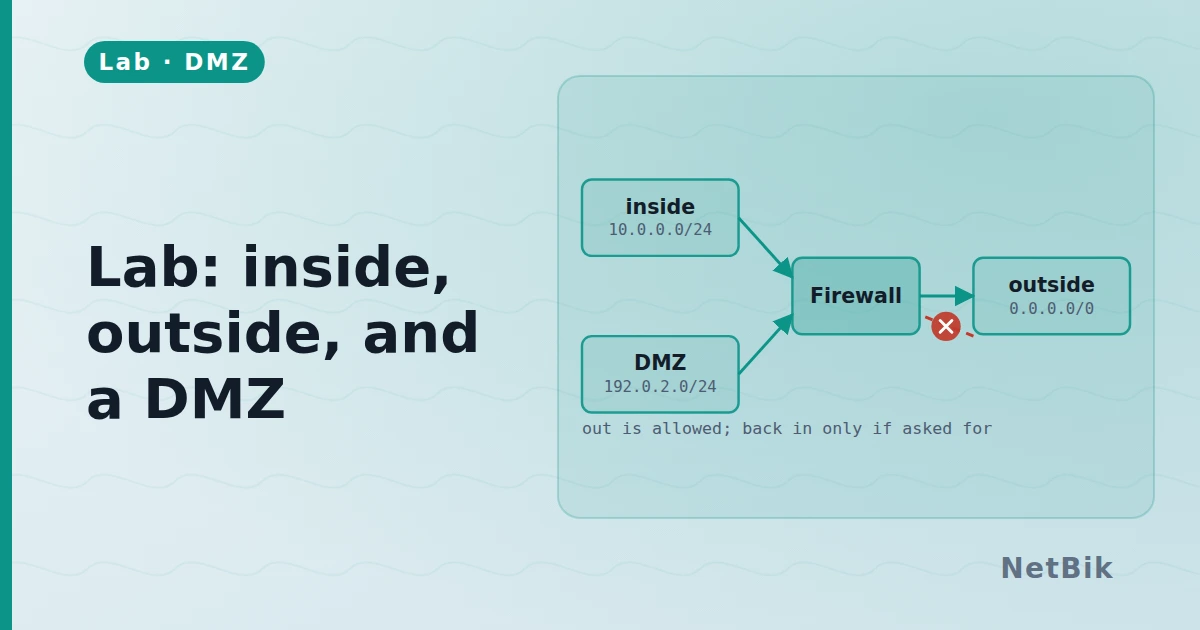
Three zones and the policies between them. A zone pair is directional, which is the whole lesson.
A zone-based firewall thinks in zones and the pairs between them, and a zone pair is one-directional. That is the thing to get into your head before you touch the configuration.
Do this
- Put each interface into a zone: inside, outside, dmz.
- Create a zone pair inside → outside and permit inspection.
- Ping out. Works.
- Ping from outside to the DMZ. It fails, because there is no zone pair in
- Add outside → dmz, permitting only the service you are publishing.
R1(config)# zone-pair security IN-OUT source inside destination outside
R1(config-sec-zone-pair)# service-policy type inspect INSIDE-POLICY
The point
No zone pair means no traffic. It is not an implicit deny in a rule list somewhere — the pair simply does not exist, so there is nothing to evaluate. That is the opposite of the ACL model, where the filter exists and the default is deny; here the filter does not exist at all.
inspect is the other half: it builds state, so the return traffic is
allowed without a second, opposite zone pair. Use pass and you will need
one.
Try breaking it
- Put two interfaces in the same zone and notice traffic between them is not
- Leave an interface in no zone and see what happens to traffic reaching it.
- Replace
inspectwithpassand find out why the replies stop.
Join the discussion
Replies, likes and bookmarks live in the community half, which needs a free account. This lab opens in the browser — no install, no plugin.
Open this in the communityEverything publishedHow this works